
A finding your engineering team can act on.
Scope, code evidence, remediation, and a clear record of what was verified. See how a public finding becomes an actionable report.
4 pages · Free download · No email required
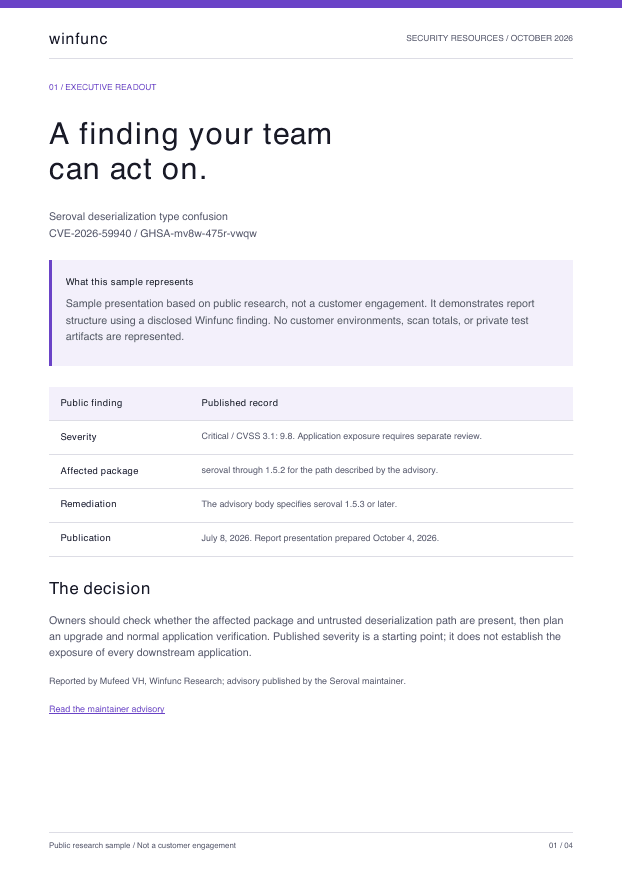
Seroval deserialization type confusion
The public advisory describes a missing internal-type check during deserialization. Affected applications accept untrusted Seroval JSON and enable relevant plugins; downstream impact depends on the behavior those plugins expose.
- Public identifier
- CVE-2026-59940 / GHSA-mv8w-475r-vwqw
- Published severity
- Critical, CVSS 3.1 9.8; application exposure still needs review
- Affected package
- seroval through 1.5.2, for the vulnerable path described in the advisory
- Remediation
- The advisory body specifies seroval 1.5.3 or later
Reported by Mufeed VH, Winfunc Research; published by the Seroval maintainer.
Sample presentation based on public research, not a customer engagement. Customer environments, scan totals, and private test artifacts are not represented.
 Preview the report ↗
Evidence before conclusions.
01Scope and preconditions
Review the installed package, untrusted input boundary, and enabled plugins before assigning application impact. No customer codebase was evaluated for this sample.
02Code evidence
The public remediation record shows a provenance check in deserializer.ts before internal Promise callbacks are used. This sample provides the patch reference without reproduction inputs.
03Proposed remediation
Use the fixed release described by the advisory, review downstream dependency resolution, and retain normal-behavior and security regression evidence through the release process.
04Verification boundary
The advisory reports that its private regression case stopped reproducing on 1.5.3. That is attributed historical evidence; preparing this sample did not independently run the test or verify a customer deployment.
Source discrepancy: the advisory’s package summary says “Patched versions: None”, while its remediation and verification sections specify 1.5.3. This sample follows the body and flags the mismatch for dependency review.
Private downstream reproduction material, payloads, credentials, and customer identifiers are omitted. No simulated scan totals or customer outcomes are presented.
Use the same evidence standard.
A two-page scorecard for agreed scope, accepted findings, reviewer time, and verified fixes. Fill it in with your own pilot results.
Download the blank pilot scorecard